MCP Gateway

One URL. Every MCP tool call your agents make, governed.
One URL. Every MCP tool call your agents make, governed.
Waxell MCP Gateway is the governance layer for AI agent tool use. Every tools/call, to GitHub, Slack, Notion, your internal APIs or anything else, flows through identity resolution, policy enforcement, fingerprinting, and audit before it reaches any upstream. Your agents keep working. You finally know what they’re doing. MCP Gateway runs on its own, and it is included in Waxell Connect.
{
  "mcpServers": {
    "waxell": {
      "url": "https://mcp-gateway.waxell.dev/mcp"
    }
  }
}
Works with Claude Cowork, Claude Desktop, Claude Code, Cursor and any MCP-compatible client. One URL replaces the upstream MCP configs on every machine.
30-minute walkthrough. No commitment.
{
  "mcpServers": {
    "waxell": {
      "url": "https://mcp-gateway.waxell.dev/mcp"
    }
  }
}
Works with Claude Cowork, Claude Desktop, Claude Code, Cursor and any MCP-compatible client. One URL replaces the upstream MCP configs on every machine.
30-minute walkthrough. No commitment.
{
  "mcpServers": {
    "waxell": {
      "url": "https://mcp-gateway.waxell.dev/mcp"
    }
  }
}
Works with Claude Cowork, Claude Desktop, Claude Code, Cursor and any MCP-compatible client. One URL replaces the upstream MCP configs on every machine.
30-minute walkthrough. No commitment.
THE PROBLEM
Every company running AI agents is running an N×M problem: N agent clients (Claude Code, Claude Desktop, Cursor, custom agents) connected to M MCP servers. Each connection authenticated separately. Every credential stored separately. Every tool call invisible to the security team.
✕ No central list of which MCP servers your team has connected
✕ Tool calls attributed to a bot account, not the person who triggered them
✕ No preventive control: governance happens after the fact, if at all
✕ Offboarding means chasing credentials across every SaaS admin console
✕ No SOC 2 evidence: "show me every tool call last quarter" has no answer
✕ MCP server updates can change tool behavior overnight, with no alert
THE ALTERNATIVE
The web got API gateways. Traffic got web application firewalls. Identity got identity-aware proxies. The shift in each case was the same: as integrations scaled faster than per-integration governance could keep up, the industry built a chokepoint.
MCP is scaling the same way. Waxell MCP Gateway is the chokepoint.
THE PROBLEM
Every company running AI agents is running an N×M problem: N agent clients (Claude Code, Claude Desktop, Cursor, custom agents) connected to M MCP servers. Each connection authenticated separately. Every credential stored separately. Every tool call invisible to the security team.
✕ No central list of which MCP servers your team has connected
✕ Tool calls attributed to a bot account, not the person who triggered them
✕ No preventive control: governance happens after the fact, if at all
✕ Offboarding means chasing credentials across every SaaS admin console
✕ No SOC 2 evidence: "show me every tool call last quarter" has no answer
✕ MCP server updates can change tool behavior overnight, with no alert
THE ALTERNATIVE
The web got API gateways. Traffic got web application firewalls. Identity got identity-aware proxies. The shift in each case was the same: as integrations scaled faster than per-integration governance could keep up, the industry built a chokepoint.
MCP is scaling the same way. Waxell MCP Gateway is the chokepoint.
What Waxell MCP Gateway Is
One MCP endpoint per tenant. You point your agents at it. Behind it, the gateway brokers to every upstream MCP server your team has configured: GitHub, Slack, Notion, Linear, internal APIs and stdio subprocesses. Every tools/call is identity-resolved, policy-checked, fingerprinted, and logged before the upstream sees it. And every result is checked again on the way back.
Your agents see one URL. Your security team sees everything.

Fingerprints:
The Rug Pull Answer
The most common MCP security failure isn't a hack. It's drift: a tool description that changes after you trusted it, adding instructions your agent now follows. A new tool that appears on a connected upstream and gets called before anyone reviews it.
The Fingerprints tab tracks every tool the gateway has seen across all connected upstreams, hashed against its name, description, and input schema. Any change triggers a status transition.
Every tool sits in one of five trust states: Pending review, Drift detected, Trusted, Blocked or Removed. A trusted tool that changes moves to Drift detected at the next discovery refresh and goes back for admin review.
Detection is automatic. Blocking is a policy you choose: with a deny_drift rule in place, MCP Gateway blocks the changed tool at call time until someone re-approves it. Waxell’s starter rule set recommends deny_drift on every upstream.
And separately: the prompt injection scanner.
Every tool description is scanned for embedded instructions at fingerprint time, before any user or agent calls the tool. If a tool description contains content that could manipulate agent behavior (the standard tool poisoning vector), it surfaces in the Risks tab as a finding with a severity rating. When a tool drifts and its description changes, the scanner runs again on the new description.
Findings stay unacknowledged until an admin reviews them. A risk_deny rule blocks any tool with an unacknowledged finding at or above the severity you set. The scan runs at rest, before any call, rather than at call time.
| Status | What it means |
|---|---|
| Pending review | Newly discovered tool — cannot be called until an admin approves it |
| Drift detected | A trusted tool changed its schema or description — resurfaces for admin review |
| Trusted | Admin has reviewed and approved this tool at its current definition |
| Blocked | Admin has explicitly blocked this tool — it cannot be called through the gateway |
| Removed | Previously advertised tool, now absent from the upstream's tool list |
Policy Gate
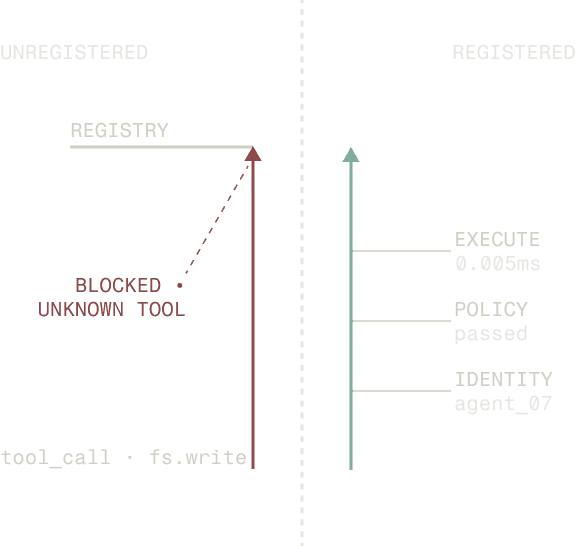
Every tools/call is evaluated against your tenant’s policy rules before the upstream sees it and again before the result returns to the agent. Rule changes take effect without a restart or redeploy.
Rules can deny a call, allow it, or hold it for approval. They can scan arguments and results for PII and credentials and then redact or block, block results that point to hosts outside an approved list, rate-limit a tool, cap its cost, and block tools that drifted or carry risk findings. A rule can target an upstream, a tool, a user, a role, a team or the specific agent acting for that user. When rules conflict, the most restrictive one wins.
One mechanic worth calling out: when a call requires approval and gets parked for review, the gateway holds the MCP connection open with progress notifications so the agent doesn't time out. When a reviewer approves, the call resumes upstream and the result returns normally. When they deny, the agent gets a structured error it can recover from. The approval pauses the agent. It doesn’t break it.
Identity & Offboarding
Every tool call through the gateway is resolved to a real user, not a service account. With on-behalf-of OAuth, the upstream’s own audit log also shows the person who triggered the call.
Each call is also tied to the agent acting for that person, so the audit log shows both, and policy can treat the same person’s research agent and ops agent differently.
Upstream auth is set per upstream. The common choices:
On-behalf-of OAuth: the gateway brokers the OAuth flow, stores the user's refresh token (KMS-encrypted, never returned to the agent client), and mints a fresh access token at call time. The upstream sees the actual user. Required for write-heavy or regulated upstreams.
Shared service account: the tenant configures one account at the org level. Gateway uses it for everyone. Fast to deploy; upstream attribution is the service account. Acceptable for low-risk reads.
Bring-your-own token: for upstreams without a standard OAuth flow. Token is stored in the credential broker, never logged, never returned to the client.
The full list of upstream auth modes is in the authentication docs.
When an employee leaves, deactivating their Waxell account revokes every per-upstream OAuth grant they held in one transaction, across every upstream at once. No per-tool chase. The audit log records the revocation event, the timestamp, the actor, and the list of upstreams unwound. The compliance artifact exists immediately.

Audit
Every tools/call MCP Gateway brokered is stored in the audit log with the resolved user, the agent, the decision and the rules that fired. The log is durable and exportable to CSV, and it stores no payloads. Retention follows your plan.
That last point matters: the audit log records what happened (who called what tool, what decision applied, which rules fired, when) without retaining the argument values or result bodies that passed through. Sensitive content is handled by the redaction pipeline. The compliance artifact proves what happened without holding the data that did.
For the compliance question “show me every tool call our agents made last quarter”, the audit log is the answer for every call routed through MCP Gateway.
1
URL per tenant
5
fingerprint trust states
2
policy checks per call
0
agent code changes
Need to keep tool calls inside your network?
The same gateway image that runs in Waxell's managed multi-tenant deployment also runs single-tenant inside your VPC. One artifact, different config. Policy decisions, credential storage, and audit data stay inside your network. Only signed health summaries flow back to Waxell.
The self-hosted version is not a separate fork. It ships at the same release cadence as the managed deployment.
On its own or inside Connect
Waxell MCP Gateway is sold on its own, for teams that want tool-call governance without a coordination layer. It is also included in Waxell Connect, so Connect customers already have tool-call policy, fingerprinting, PII scanning and the tool-call audit log.
The capability is the same either way. Connect adds agent registration, shared workspaces, hand-offs and the human-in-the-loop inbox on top. See Waxell Connect.
What Waxell MCP Gateway Is
One MCP endpoint per tenant. You point your agents at it. Behind it, the gateway brokers to every upstream MCP server your team has configured: GitHub, Slack, Notion, Linear, internal APIs and stdio subprocesses. Every tools/call is identity-resolved, policy-checked, fingerprinted, and logged before the upstream sees it. And every result is checked again on the way back.
Your agents see one URL. Your security team sees everything.
How to get started
01
Point your clients at the gateway
Replace the upstream MCP server entries in Claude, Cursor or any MCP client with your MCP Gateway URL. Agent logic and prompts stay the same.
02
Connect upstreams from the catalog
Install upstreams from the connector catalog, or add your own internal MCP servers. Each person connects their own accounts once, through your tenant.
03
Turn on policy and audit
Start from the starter rule set, including deny_drift, then add rules by upstream, tool, team or agent. Every call lands in the audit log from the first request.
01
Point your clients at the gateway
Replace the upstream MCP server entries in Claude, Cursor or any MCP client with your MCP Gateway URL. Agent logic and prompts stay the same.
02
Connect upstreams from the catalog
Install upstreams from the connector catalog, or add your own internal MCP servers. Each person connects their own accounts once, through your tenant.
03
Turn on policy and audit
Start from the starter rule set, including deny_drift, then add rules by upstream, tool, team or agent. Every call lands in the audit log from the first request.
Fingerprints:
The Rug Pull Answer
The most common MCP security failure isn't a hack. It's drift: a tool description that changes after you trusted it, adding instructions your agent now follows. A new tool that appears on a connected upstream and gets called before anyone reviews it.
The Fingerprints tab tracks every tool the gateway has seen across all connected upstreams, hashed against its name, description, and input schema. Any change triggers a status transition.
Every tool sits in one of five trust states: Pending review, Drift detected, Trusted, Blocked or Removed. A trusted tool that changes moves to Drift detected at the next discovery refresh and goes back for admin review.
Detection is automatic. Blocking is a policy you choose: with a deny_drift rule in place, MCP Gateway blocks the changed tool at call time until someone re-approves it. Waxell’s starter rule set recommends deny_drift on every upstream.
And separately: the prompt injection scanner.
Every tool description is scanned for embedded instructions at fingerprint time, before any user or agent calls the tool. If a tool description contains content that could manipulate agent behavior (the standard tool poisoning vector), it surfaces in the Risks tab as a finding with a severity rating. When a tool drifts and its description changes, the scanner runs again on the new description.
Findings stay unacknowledged until an admin reviews them. A risk_deny rule blocks any tool with an unacknowledged finding at or above the severity you set. The scan runs at rest, before any call, rather than at call time.
Fingerprints:
The Rug Pull Answer
The most common MCP security failure isn't a hack. It's drift: a tool description that changes after you trusted it, adding instructions your agent now follows. A new tool that appears on a connected upstream and gets called before anyone reviews it.
The Fingerprints tab tracks every tool the gateway has seen across all connected upstreams, hashed against its name, description, and input schema. Any change triggers a status transition.
Every tool sits in one of five trust states: Pending review, Drift detected, Trusted, Blocked or Removed. A trusted tool that changes moves to Drift detected at the next discovery refresh and goes back for admin review.
Detection is automatic. Blocking is a policy you choose: with a deny_drift rule in place, MCP Gateway blocks the changed tool at call time until someone re-approves it. Waxell’s starter rule set recommends deny_drift on every upstream.
And separately: the prompt injection scanner.
Every tool description is scanned for embedded instructions at fingerprint time, before any user or agent calls the tool. If a tool description contains content that could manipulate agent behavior (the standard tool poisoning vector), it surfaces in the Risks tab as a finding with a severity rating. When a tool drifts and its description changes, the scanner runs again on the new description.
Findings stay unacknowledged until an admin reviews them. A risk_deny rule blocks any tool with an unacknowledged finding at or above the severity you set. The scan runs at rest, before any call, rather than at call time.
| Status | What it means |
|---|---|
| Pending review | Newly discovered tool — cannot be called until an admin approves it |
| Drift detected | A trusted tool changed its schema or description — resurfaces for admin review |
| Trusted | Admin has reviewed and approved this tool at its current definition |
| Blocked | Admin has explicitly blocked this tool — it cannot be called through the gateway |
| Removed | Previously advertised tool, now absent from the upstream's tool list |
Policy Gate
Every tools/call is evaluated against your tenant’s policy rules before the upstream sees it and again before the result returns to the agent. Rule changes take effect without a restart or redeploy.
Rules can deny a call, allow it, or hold it for approval. They can scan arguments and results for PII and credentials and then redact or block, block results that point to hosts outside an approved list, rate-limit a tool, cap its cost, and block tools that drifted or carry risk findings. A rule can target an upstream, a tool, a user, a role, a team or the specific agent acting for that user. When rules conflict, the most restrictive one wins.
One mechanic worth calling out: when a call requires approval and gets parked for review, the gateway holds the MCP connection open with progress notifications so the agent doesn't time out. When a reviewer approves, the call resumes upstream and the result returns normally. When they deny, the agent gets a structured error it can recover from. The approval pauses the agent. It doesn’t break it.
Identity & Offboarding
Every tool call through the gateway is resolved to a real user, not a service account. With on-behalf-of OAuth, the upstream’s own audit log also shows the person who triggered the call.
Each call is also tied to the agent acting for that person, so the audit log shows both, and policy can treat the same person’s research agent and ops agent differently.
Upstream auth is set per upstream. The common choices:
On-behalf-of OAuth: the gateway brokers the OAuth flow, stores the user's refresh token (KMS-encrypted, never returned to the agent client), and mints a fresh access token at call time. The upstream sees the actual user. Required for write-heavy or regulated upstreams.
Shared service account: the tenant configures one account at the org level. Gateway uses it for everyone. Fast to deploy; upstream attribution is the service account. Acceptable for low-risk reads.
Bring-your-own token: for upstreams without a standard OAuth flow. Token is stored in the credential broker, never logged, never returned to the client.
The full list of upstream auth modes is in the authentication docs.
When an employee leaves, deactivating their Waxell account revokes every per-upstream OAuth grant they held in one transaction, across every upstream at once. No per-tool chase. The audit log records the revocation event, the timestamp, the actor, and the list of upstreams unwound. The compliance artifact exists immediately.
Audit
Every tools/call MCP Gateway brokered is stored in the audit log with the resolved user, the agent, the decision and the rules that fired. The log is durable and exportable to CSV, and it stores no payloads. Retention follows your plan.
That last point matters: the audit log records what happened (who called what tool, what decision applied, which rules fired, when) without retaining the argument values or result bodies that passed through. Sensitive content is handled by the redaction pipeline. The compliance artifact proves what happened without holding the data that did.
For the compliance question “show me every tool call our agents made last quarter”, the audit log is the answer for every call routed through MCP Gateway.
1
URL per tenant
5
fingerprint trust states
2
policy checks per call
0
agent code changes
Need to keep tool calls inside your network?
The same gateway image that runs in Waxell's managed multi-tenant deployment also runs single-tenant inside your VPC. One artifact, different config. Policy decisions, credential storage, and audit data stay inside your network. Only signed health summaries flow back to Waxell.
The self-hosted version is not a separate fork. It ships at the same release cadence as the managed deployment.
On its own or inside Connect
Waxell MCP Gateway is sold on its own, for teams that want tool-call governance without a coordination layer. It is also included in Waxell Connect, so Connect customers already have tool-call policy, fingerprinting, PII scanning and the tool-call audit log.
The capability is the same either way. Connect adds agent registration, shared workspaces, hand-offs and the human-in-the-loop inbox on top. See Waxell Connect.
How to get started
01
Point your clients at the gateway
Replace the upstream MCP server entries in Claude, Cursor or any MCP client with your MCP Gateway URL. Agent logic and prompts stay the same.
02
Connect upstreams from the catalog
Install upstreams from the connector catalog, or add your own internal MCP servers. Each person connects their own accounts once, through your tenant.
03
Turn on policy and audit
Start from the starter rule set, including deny_drift, then add rules by upstream, tool, team or agent. Every call lands in the audit log from the first request.
How to get started
01
Point your clients at the gateway
Replace the upstream MCP server entries in Claude, Cursor or any MCP client with your MCP Gateway URL. Agent logic and prompts stay the same.
02
Connect upstreams from the catalog
Install upstreams from the connector catalog, or add your own internal MCP servers. Each person connects their own accounts once, through your tenant.
03
Turn on policy and audit
Start from the starter rule set, including deny_drift, then add rules by upstream, tool, team or agent. Every call lands in the audit log from the first request.
Your agents are already calling tools.
The Waxell MCP Gateway gives you governance over which ones, and a record that proves you had it.
30-minute walkthrough. No commitment.
FAQ
What is the Waxell MCP Gateway?
How does Waxell MCP Gateway protect against rug pulls?
Is MCP Gateway included in Waxell Connect?
What happens if the Waxell MCP Gateway goes down?
How does MCP Gateway relate to Waxell Observe?
Is there a self-hosted option for the Waxell MCP Gateway?
Deploying Waxell? See how teams roll it out.
Your agents are already calling tools.
The Waxell MCP Gateway gives you governance over which ones, and a record that proves you had it.
30-minute walkthrough. No commitment.
FAQ
What is the Waxell MCP Gateway?
How does Waxell MCP Gateway protect against rug pulls?
Is MCP Gateway included in Waxell Connect?
What happens if the Waxell MCP Gateway goes down?
How does MCP Gateway relate to Waxell Observe?
Is there a self-hosted option for the Waxell MCP Gateway?
Deploying Waxell? See how teams roll it out.
Waxell
Waxell provides observability and governance for AI agents in production. Bring your own framework.
Compliance: NIST AI RMF · EU AI Act · SOC 2 compliant · ISO/IEC 27001:2022 certified · HIPAA (in progress)
Governed continuously in Vanta.
© 2026 Waxell. All rights reserved.
Patent Pending.
Waxell
Waxell provides observability and governance for AI agents in production. Bring your own framework.
Compliance: NIST AI RMF · EU AI Act · SOC 2 compliant · ISO/IEC 27001:2022 certified · HIPAA (in progress)
Governed continuously in Vanta.
© 2026 Waxell. All rights reserved.
Patent Pending.
Waxell
Waxell provides observability and governance for AI agents in production. Bring your own framework.
Compliance: NIST AI RMF · EU AI Act · SOC 2 compliant · ISO/IEC 27001:2022 certified · HIPAA (in progress)
Governed continuously in Vanta.
© 2026 Waxell. All rights reserved.
Patent Pending.